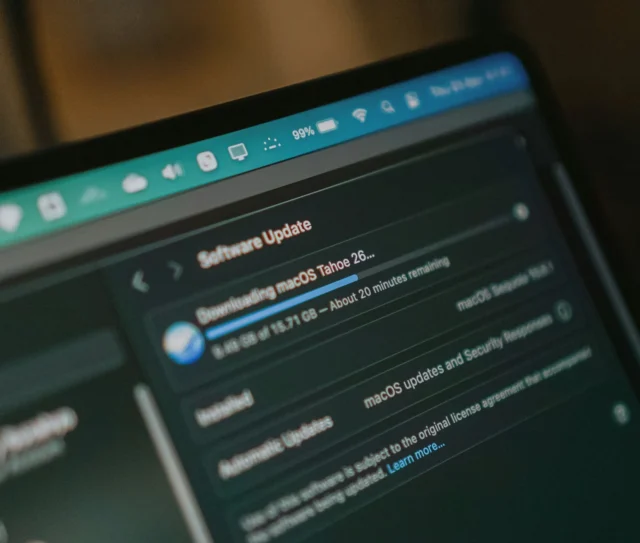
Apple’s iOS and macOS 26.5 public release is expected this week. For most people, it is a routine update. For businesses with managed devices, “routine” can still mean a disrupted morning if it is not handled properly. Here is what to do before it lands.
The Release Candidate dropped on 4 May, which means the final build is essentially ready. IT managers and ops directors have a narrow window to get ahead of this. Not because 26.5 is a high-risk update, but because the businesses that handle updates well are the ones with a process in place before the prompt appears on screen.
What is actually in iOS and macOS 26.5
This is a maintenance release. If you were expecting significant new features, they are not here. Apple’s attention has shifted toward iOS 27 and WWDC in June.
What is in 26.5:
- End-to-end encrypted RCS messaging (beta) – Messages sent between iPhone and Android users can now be encrypted end-to-end, with supported carriers. The feature is enabled by default and can be managed via Settings > Messages > RCS Messaging. For mixed iPhone/Android teams, this is a meaningful privacy improvement for business communications over RCS. It is in beta, and rollout will be gradual depending on carrier support.
- Security patches and bug fixes – The primary reason to update, and the reason not to delay indefinitely.
- Suggested Places in Apple Maps – Recommendations based on trending locations and recent searches. Low business relevance, but worth noting as it arrives alongside Maps advertising, which Apple is introducing alongside 26.5.
- No major feature disruption – This is not an update that changes how your team works. The risk profile is low.
What is the actual risk for a managed Mac fleet?
The risk from macOS 26.5 itself is low, but the operational risk of an unmanaged rollout is not. The update is unlikely to break anything significant. The real disruption comes from sixty people simultaneously prompted to update at 9 am on a Monday: devices restarting mid-meeting, apps closing without warning, and a spike in helpdesk calls from people who clicked “update now” without thinking.
A few specific areas worth assessing before deployment:
Third-party app compatibility
Before rolling out fleet-wide, check whether any critical applications in your stack have known issues with 26.5. Adobe, Microsoft 365, and project management tools are the usual suspects. Check vendor release notes and forums in the days following the public release before pushing to all devices.
Intel Macs in your fleet
macOS Tahoe is the final version of macOS that will support Intel-based Macs. Each point update narrows the support window. If you have 2019 or 2020 Intel machines still in use, 26.5 is a prompt to think about timelines, not a reason to avoid updating, but a flag that fleet planning is increasingly urgent.
The security patch window
The time between Apple publishing a security update and active exploitation of the patched vulnerability is getting shorter. This is not a reason to update immediately without testing, but it is a reason not to sit on it for weeks.
The pre-update checklist: what to do before it goes live
1. Use MDM to pause automatic updates
If you are running Jamf, Addigy, or the Apple Business DMS (Device Management Service), configure your update policy to defer the public release while you test. This gives you control over timing without blocking security patches indefinitely.
2. Test on a non-critical device first
Before deploying fleet-wide, install 26.5 on one machine that is not in active daily use. Run through the applications your team depends on. Check for anything unexpected. Twenty minutes of testing can prevent hours of helpdesk calls.
3. Check critical app compatibility
Go through your key applications – email, collaboration tools, finance software, design tools, and check vendor release notes for known 26.5 issues. Most major vendors respond quickly to Apple releases. If something flags, hold deployment on affected device groups until a patch is available.
4. Audit Intel Macs in the fleet
Pull a list of any devices running Intel-based hardware. These are the machines with the shortest remaining support runway. If they are in regular business use, now is the time to discuss upgrade timelines with decision-makers.
5. Communicate to staff before the prompt appears
Tell your team when the update is coming, what to expect (a restart, a few minutes of downtime), and who to contact if something does not look right afterwards. A brief message the day before prevents most of the confusion.
6. Schedule the rollout for a Tuesday or Wednesday
Avoid Mondays (high meeting load) and Fridays (no one wants to troubleshoot at 4 pm ahead of a weekend). Mid-week gives you a full working day to respond to anything unexpected.
7. Verify FileVault and MDM enrolment status before updating
A device that loses MDM enrolment during an update is a security and compliance event. Check that all devices are fully enrolled and that FileVault is active before the rollout begins.
8. Confirm your rollback plan
In the unlikely event that something does break, know the process before you need it – whether that is restoring from a backup, rolling back via MDM policy, or escalating to support.
If you Do not have MDM: what that means right now
If your business is managing its Mac fleet without MDM, whether that is because it grew quickly, inherited devices, or has simply not got around to it, a point update like 26.5 makes the gap visible.
Without MDM, you have no control over when individual devices update. A team member away from the office, a device on automatic updates, or someone who clicks “install now” on a Tuesday morning all sit outside your visibility. You cannot confirm what build is running across your fleet, you cannot remotely remediate a device that has a post-update issue, and you cannot enforce a phased rollout.
For a minor release like 26.5, this is manageable, if uncomfortable. For a larger update, or for a business working toward Cyber Essentials or ISO 27001, the absence of MDM is increasingly difficult to explain. In Dr Logic’s experience, the businesses that struggle most with Apple updates are not the ones with complex fleets; they are the ones that have never formalised how updates are managed at all.If that describes your situation, IT Support and Apple and Hybrid IT Support are the right starting points. The infrastructure to manage this properly is not complex to put in place.
What to monitor after the update
The first 24 hours after deployment are the most important window – most post-update issues surface quickly if you know what to look for.
MDM check-ins
Confirm that all devices have updated to the correct build and that enrolment is intact. Any device that has not checked in after updating warrants a follow-up.
Devices that did not update
Identify why: low storage, a dismissed prompt, a compatibility hold, and resolve each case individually rather than leaving stragglers on an older build indefinitely.
Helpdesk patterns
Monitor incoming requests on the first day for anything that repeats. A single user with an issue is a coincidence. Three users with the same issue after an update is a pattern worth investigating before it spreads.
RCS messaging
If your team uses Messages for business communication and includes Android users, the end-to-end RCS encryption feature is now active by default. Worth a brief note to staff so they understand what has changed, and what it means for how their messages are handled in transit.
If you need help managing macOS and iOS updates across your Mac fleet, talk to Dr Logic. We provide IT Support and IT Strategy tailored to Apple environments, and if your team is still updating Macs by telling everyone to check Settings, it might be time to talk about what a managed Apple environment actually looks like.
Related articles
- Do You Still Need a Third-Party MDM Now That Apple Business Is Free?
- What Cyber Essentials Certification Actually Looks Like for an All-Mac Office
- Dr Logic Achieves Apple Premium Technical Partner Status: What It Means for Your Business
FAQs
When is macOS and iOS 26.5 being released?
The Release Candidate was seeded on 4 May 2026, and the public release is expected around 11 May. If you are managing a business fleet, use that window to test compatibility and prepare a controlled rollout rather than letting devices update automatically on day one.
Do I need to update to macOS 26.5 straight away?
Not immediately, but do not delay for long. The update contains security patches, and the window between Apple publishing a fix and active exploitation of the vulnerability it addresses is getting shorter. Test on a non-critical device first, check critical app compatibility, then deploy within a week or two of the public release.
What does macOS 26.5 mean for Intel Macs in my business?
macOS 26 Tahoe is the last version of macOS to support Intel-based Macs. From macOS 27, Intel hardware will not be supported. If you still have Intel Macs in regular business use, each update is a reminder that the upgrade window is narrowing. Now is the time to plan replacements, not to avoid updating, but to avoid being caught unprepared when support ends entirely.