Having a breach reporting policy and having someone actively coordinate that reporting during a live incident are not the same thing. A policy tells you what should happen. Coordination is what actually happens once the deadline is real, the facts are incomplete, and more than one party needs to be brought in at once: your insurer, their incident response team, and the regulator.
Under UK GDPR, a notifiable personal data breach must be reported to the Information Commissioners Office (ICO) within 72 hours of the organisation becoming aware of it. That much is well known. What is less understood is what has to happen inside that window, and what changes once a cyber insurance policy and an incident response team are involved.
Having a policy is not the same as having someone coordinate it under pressure
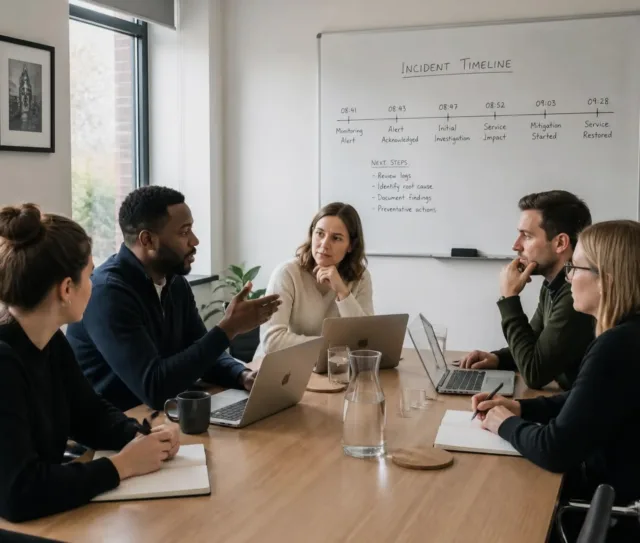
A breach reporting policy on paper answers one question: what should we do. Active coordination answers a harder one: who is doing it, right now, while an insurer’s incident response team is asking for evidence and the clock is already running.
A document versus active coordination with your insurer’s IR team
Most cyber insurance policies include access to an incident response team as part of the cover, not as an optional extra. That team typically leads containment, evidence gathering, and communication with the regulator on the insured’s behalf. A business that has never used this service before an incident often does not know how quickly that team can be reached, what they need from you first, or how their process fits alongside your own. Establishing that beforehand, not during the first hour of a live incident, is what turns a policy into something that actually works under pressure.
You don’t want to be improvising this during a live incident
Dr Logic can help you build direct coordination with your insurer’s incident response team before you ever need it.
The 72-hour ICO window has specific, sequenced requirements
The 72-hour clock starts when the organisation becomes aware of the breach, regardless of whether the investigation is complete. An initial notification can be submitted with incomplete information, provided it is followed up as more detail emerges.
What “aware” means and when the clock starts
Awareness means reaching a reasonable degree of confidence that a security incident has compromised personal data, even before the full technical picture is known. A report from an employee, a third-party alert, or law enforcement contact can all start the clock, regardless of whether your own investigation has confirmed the details yet.
What evidence needs to be ready before you notify
An ICO notification needs a description of the breach, the likely consequences, and the measures taken or proposed to address it. Gathering this within 72 hours is far more manageable when an incident log has been kept from the first hour, rather than reconstructed under deadline pressure once the notification is due.
An incomplete first notification is acceptable, and the ICO expects this in practice. What matters is that the initial submission is followed by updates as the picture becomes clearer, rather than the business going quiet until it has every answer. Businesses that wait for full certainty before making contact are the ones most likely to miss the deadline entirely, because full certainty rarely arrives within 72 hours of a serious incident.
What changes if you have US-based team members or clients
Where a business has team members or clients based in the US, a UK data breach can trigger a second, separate regulatory clock alongside the ICO deadline. US state-level breach notification laws vary by state, and several carry shorter or differently triggered deadlines than the UK’s 72-hour window. Coordinating both obligations at once, rather than treating the UK notification as the only one that matters, is what a genuinely joined-up incident response service should cover.
UK-only reporting compared with UK and US reporting
| Aspect | UK-only obligation | UK plus US obligation |
|---|---|---|
| Primary regulator | ICO | ICO, plus relevant US state regulators |
| Reporting window | 72 hours from awareness | 72 hours for the ICO; US state deadlines vary and can be shorter |
| Trigger for the clock | Awareness of a likely breach | Awareness, assessed separately against each jurisdiction's threshold |
| Coordination need | Single regulator, single timeline | Two timelines running in parallel, requiring coordinated evidence |
In Dr Logic’s experience, the businesses that struggle most during a live breach are not the ones without cyber insurance. They are the ones who have never actually spoken to their insurer’s incident response team before the day they need them, and who discover mid-incident that a second regulatory clock is running alongside the one they already knew about.
If your business has never tested how quickly your insurer’s incident response team can be reached, or is unsure what changes if US-based team members or clients are involved, Dr Logic’s cyber security team can help you build that coordination in before it is needed.
Related articles
- Your breach reporting policy may be weaker than you think
- What Cyber Essentials certification actually looks like for an all-Mac office
FAQs
What is the 72-hour rule under UK GDPR?
The 72-hour rule requires organisations to notify the ICO of a notifiable personal data breach within 72 hours of becoming aware of it. The clock starts from awareness, not from when a full investigation is complete, and an initial notification can be submitted with incomplete information.
What is the difference between a breach reporting policy and insurer coordination?
A policy describes what should happen during a breach. Insurer coordination is the live process of working with your insurer’s incident response team to manage containment, evidence, and regulatory notification in real time. A business only discovers whether the two work together during an actual incident.
Does having cyber insurance change what I need to report?
No. Cyber insurance does not change your legal obligation to notify the ICO within 72 hours. It typically adds access to an incident response team that can help you meet that obligation, provided the coordination has been established before an incident occurs.
What changes if my business has US-based team members or clients?
A UK data breach involving US-based team members or clients can trigger separate US state-level notification obligations alongside the UK’s 72-hour ICO deadline. These deadlines vary by state and are not automatically covered by UK-focused breach response planning.
How quickly should I expect to hear back from my insurer's incident response team?
This varies by policy and provider, and should be confirmed directly with your insurer before an incident happens. Establishing contact details and expected response times in advance removes uncertainty at the exact moment it matters most.